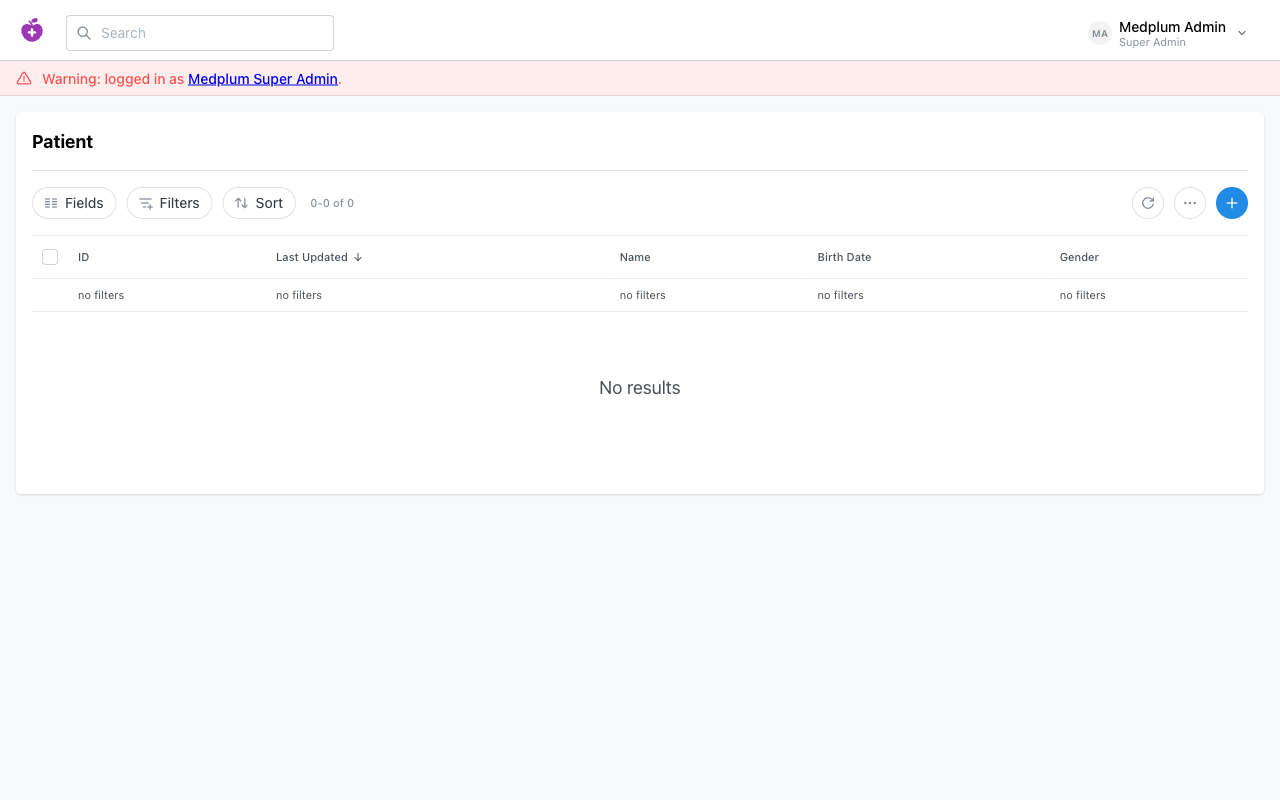
After signing in · Oct 21, 2026Sign-in page · Oct 21, 2026
About this app
A toolkit for building health record apps on the FHIR standard; a developer platform, not a ready-made chart.
Tested by Langford on Oct 21, 2026: Started from the project's published images and signed in as a new admin; the page showed "Patient". Read the test report
What it replaces
Healthie
Canvas (FHIR platform)
Information
Made by
Run and supported by Langford; built on open-source software
Category
Run a medical practice
Edition
Developer (one of 2 editions of Langford Practice)
Licence
Apache-2.0
Data you can keep
Built for sensitive data with setup: Ships a default admin login (admin@example.com) that must be changed.
Free for your business
Yes. Free open-source licence (Apache-2.0).
Suits
Healthcare
Tested on
Oct 21, 2026
Built on Medplum, open-source software (Apache-2.0). Source available.
Other editions of Langford Practice
Clinic editionPatient charts, scheduling, prescriptions and billing for a medical practice.
Built for sensitive data with setup. Ships a default admin login (admin@example.com) that must be changed.
What “Tested” means
Started from the project's published images and signed in as a new admin; the page showed "Patient". Testing shows the app starts and signs in. It is not a security audit.
I run a:
Rules this helps you meet:HIPAA Security Rule — The safeguards apply once we host it
We don't sign Business Associate Agreements (BAAs) yet. Don't store patient health information until we do.
If your practice keeps patient health information (PHI, or ePHI once it is electronic), these are the HIPAA Security Rule technical safeguards this hosting covers on our side for Langford Practice · Developer, and the parts that stay with the practice.
What your examiner or auditor will ask
Access control: can only the right people and systems reach ePHI?
On our side, yes: the database has no public address, the app holds no cloud keys, and its passwords live in a vault. Who sees which patient inside the app is set by the practice through user roles.
Our hosting logs every database and storage access to a separate archive kept 6 years. A per-user activity screen inside the app depends on the app; our built-in one is designed, not built.
BuiltDesigned, not builtEvidence: the checks below · our control listCovers on our side: HIPAA Security Rule (45 CFR 164.312(b))
Integrity: can records be changed or destroyed improperly without anyone knowing?
Partly covered. Changes are logged, the audit archive is write-once, and backups let us roll back 35 days. We have not mapped a control to this safeguard yet, so treat it as open.